
Multiple named security keys / passkeys per user + choosing the 2FA method at login

-
Passkey support in Cloudron 10 works well for me: passwordless login with a Nitrokey, including the PIN prompt, works fine. Thanks!
What's missing for hardware keys: each user can only have one passkey and one TOTP (screenshot 1). With hardware keys you normally register at least two, one for daily use and a backup kept somewhere safe. Today, losing that one key means an admin has to reset 2FA.
Request:
-
Multiple passkeys per user.
-
A name per key (e.g. "Nitrokey office", "Nitrokey backup"), listed in the profile with date added / last used, and each removable on its own.
-
After choosing "security key", a selector to pick the key would be great. If needed, I can provide a login flow from a service that does it nicely.
-
Keep both login paths as they are: passwordless (FIDO2) with key + PIN, or username/password with TOTP or the key as second factor.
-
Optional: accounts that use only a hardware/FIDO2 key and have no password at all. Is that possible? Would really be great.
-
Optional: The login page is good, but a more prominent passkey/FIDO2-only option would be nice.
Somewhat related: https://forum.cloudron.io/topic/15932/login-with-totp-vs-passkey
Thanks!
Tim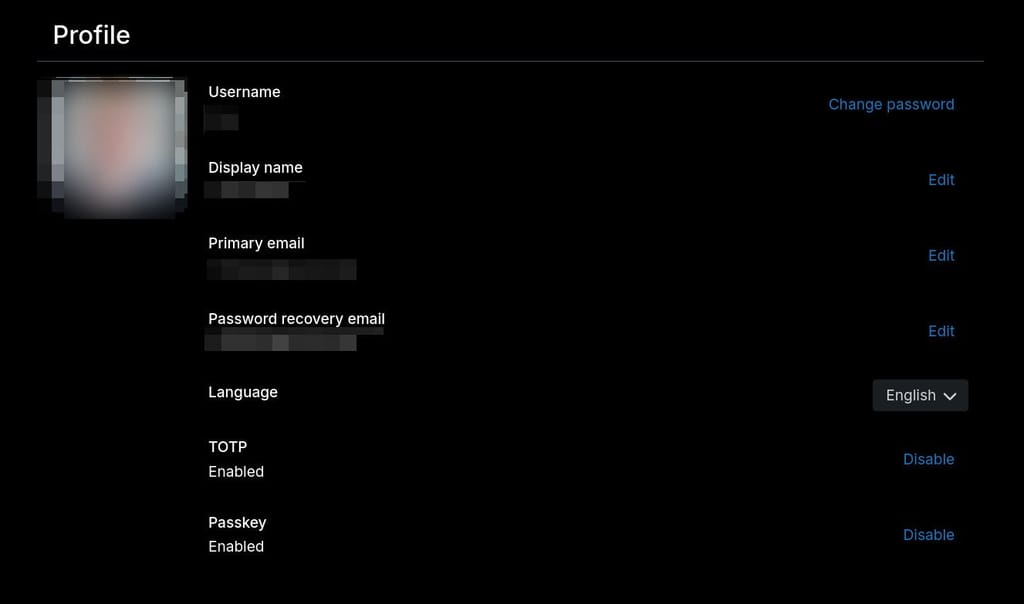
-
-
Also: shouldn’t we be able to disable login via Password when Passkeys are enabled? Given that Passkeys are much more secure: Why should we leave open the insecure option to login via password?
-
I think supporting more than one does make sense. I will make a work item for this in gitlab so we can add this in some time.
Why should we leave open the insecure option to login via password?
I don't think password login is still open, after entering the username+password it should always ask for the 2fa auth if setup. There is also the passkey option to skip username+password+2fa altogether as passkey can also identify the user, for this you can just click the "Login with passkey" label below the login form.

Hello! It looks like you're interested in this conversation, but you don't have an account yet.
Getting fed up of having to scroll through the same posts each visit? When you register for an account, you'll always come back to exactly where you were before, and choose to be notified of new replies (either via email, or push notification). You'll also be able to save bookmarks and upvote posts to show your appreciation to other community members.
With your input, this post could be even better 💗
Register Login