Cloudron makes it easy to run web apps like WordPress, Nextcloud, GitLab on your server. Find out more or install now.


Skip to content
  • Categories
  • Recent
  • Tags
  • Popular
  • Bookmarks
  • Search
Skins
  • Light
  • Brite
  • Cerulean
  • Cosmo
  • Flatly
  • Journal
  • Litera
  • Lumen
  • Lux
  • Materia
  • Minty
  • Morph
  • Pulse
  • Sandstone
  • Simplex
  • Sketchy
  • Spacelab
  • United
  • Yeti
  • Zephyr
  • Dark
  • Cyborg
  • Darkly
  • Quartz
  • Slate
  • Solar
  • Superhero
  • Vapor

  • Default (No Skin)
  • No Skin
Collapse
Brand Logo

Cloudron Forum

Offical apps | Community apps | Demo | Docs | Install
marcusquinnM

marcusquinn

@marcusquinn
CA Maintainer Super Fan
Unfollow Follow
About
Posts
3.4k
Topics
449
Shares
0
Groups
2
Followers
9
Following
2

Posts

Recent Best Controversial

  • VPN protection: allow other VPN apps (WireGuard, NetBird, ...) as the VPN app (small patch)
    marcusquinnM marcusquinn
    Feature Requests

    Apologies for having AI write it, but probably writes better than me, now:

    Hi @girish @nebulon,

    Thanks for VPN protection, and for the new allowlist. I'm maintaining the NetBird community package (self-hosted WireGuard mesh). Several of its users would like to protect Cloudron apps with NetBird instead of running OpenVPN alongside it.

    I read through platform/box master (c36346e). The only OpenVPN-specific part is how the VPN app is selected. The rest is already provider-neutral:

    • reverseproxy.js allows the selected app's container IPv4/IPv6, then deny all
    • app-bridge.js /vpn-access-config serves split-DNS data to whichever app is selected
    • apptask.js clears the policy when that app is uninstalled

    Selection is checked against io.cloudron.openvpn in four places: network.js:setVpnAccessConfig, apps.js:setVpnAccess, VpnAccess.vue and Access.vue.

    Proposal: accept any app with the net_admin capability as the VPN app. Any app that routes VPN traffic needs that capability anyway, and the admin still has to pick it explicitly in Network > VPN access. That is the same trust decision as picking OpenVPN today. The patch also blocks only the selected VPN app (rather than every OpenVPN app) from requiring VPN access, and refuses to select an app that is itself protected.

    It needs no change to manifest-format. If you'd rather have an explicit opt-in, a new vpn capability in @cloudron/manifest-format would work just as well with the same box changes. I'm happy to rework it either way.

    On the NetBird side, the plan is a separate small "routing peer" app (net_admin, masquerades mesh traffic to the Cloudron host). It would not be the management server, because that container also runs public services and must not be trusted as VPN ingress. NetBird policies would then decide which user groups can reach the protected apps. They act on the whole set, though, because every protected app shares the host's IP.

    Testing: I added cases to src/test/network-test.js. ESLint is clean on the changed files, apart from an existing no-use-before-define at apps.js:520, and the dashboard builds. I couldn't run the mocha suite because its setup needs your Linux sudo scripts, so please treat the tests as unrun.

    diff --git a/dashboard/src/components/app/Access.vue b/dashboard/src/components/app/Access.vue
    index d04b9bf..506dc19 100644
    --- a/dashboard/src/components/app/Access.vue
    +++ b/dashboard/src/components/app/Access.vue
    @@ -14,8 +14,6 @@ import UsersModel from '../../models/UsersModel.js';
     import GroupsModel from '../../models/GroupsModel.js';
     import { requestError, selectOptionsFromUsers } from '../../utils.js';
     
    -const OPENVPN_APP_APPSTORE_ID = 'io.cloudron.openvpn';
    -
     const props = defineProps([ 'app', 'refreshApp' ]);
     
     const features = inject('features');
    @@ -35,8 +33,10 @@ const accessRestrictionAcl = ref({ users: [], groups: [] });
     const operatorAcl = ref({ users: [], groups: [] });
     const requiresVpn = ref(false);
     const vpnProtectionEnabled = ref(false);
    +const selectedVpnAppId = ref(null);
     
    -const showRequireVpn = computed(() => props.app.manifest?.id !== OPENVPN_APP_APPSTORE_ID && features.value.vpnProtection);
    +// the selected VPN app is the trusted ingress, so it cannot itself be VPN protected
    +const showRequireVpn = computed(() => features.value.vpnProtection && props.app.id !== selectedVpnAppId.value);
     
     function allowlistHasEntry(text) {
       return (text || '').split('\n').some((line) => line.length !== 0 && line[0] !== '#');
    @@ -113,9 +113,10 @@ onMounted(async () => {
     
       requiresVpn.value = !!props.app.requiresVpn;
     
    -  if (showRequireVpn.value) {
    +  if (features.value.vpnProtection) {
         [error, result] = await networkModel.getVpnAccessConfig();
         if (error) return console.error(error);
    +    selectedVpnAppId.value = result.vpnAppId || null;
         vpnProtectionEnabled.value = !!result.vpnAppId || allowlistHasEntry(result.allowlist);
       }
     });
    diff --git a/dashboard/src/components/network/VpnAccess.vue b/dashboard/src/components/network/VpnAccess.vue
    index f0079bf..b845ecd 100644
    --- a/dashboard/src/components/network/VpnAccess.vue
    +++ b/dashboard/src/components/network/VpnAccess.vue
    @@ -13,6 +13,11 @@ const { t } = useI18n();
     
     const OPENVPN_APP_APPSTORE_ID = 'io.cloudron.openvpn';
     
    +// keep in sync with apps.isVpnProvider() in the box code
    +function isVpnProvider(manifest) {
    +  return manifest?.id === OPENVPN_APP_APPSTORE_ID || (manifest?.capabilities || []).includes('net_admin');
    +}
    +
     // UI presets map onto the two-mode wire model: full | custom(+cidrs) | custom(no cidrs)
     const ROUTING_FULL = 'full';
     const ROUTING_APPS_ONLY = 'apps-only';
    @@ -107,7 +112,7 @@ async function loadData() {
       installedApps.value = apps;
     
       vpnApps.value = apps
    -    .filter((app) => app.manifest?.id === OPENVPN_APP_APPSTORE_ID)
    +    .filter((app) => isVpnProvider(app.manifest) && !app.requiresVpn)
         .map((app) => ({ id: app.id, label: app.label || app.fqdn || app.id }));
     
       [error, apps] = await networkModel.getVpnAccessConfig();
    diff --git a/src/apps.js b/src/apps.js
    index d2f0b4e..a042f55 100644
    --- a/src/apps.js
    +++ b/src/apps.js
    @@ -1150,15 +1150,22 @@ async function setOperators(app, operators, auditSource) {
         await eventlog.add(eventlog.ACTION_APP_CONFIGURE, auditSource, { appId, app, operators });
     }
     
    +// an app can be selected as the VPN app if it can route traffic (OpenVPN, WireGuard, NetBird, ...).
    +// the admin still has to select it explicitly, after which its container IPs are trusted as VPN ingress
    +function isVpnProvider(manifest) {
    +    assert.strictEqual(typeof manifest, 'object');
    +
    +    return manifest.id === constants.OPENVPN_APP_APPSTORE_ID || (manifest.capabilities || []).includes('net_admin');
    +}
    +
     async function setVpnAccess(app, enable, auditSource) {
         assert.strictEqual(typeof app, 'object');
         assert.strictEqual(typeof enable, 'boolean');
         assert.strictEqual(typeof auditSource, 'object');
     
    -    if (app.manifest.id === constants.OPENVPN_APP_APPSTORE_ID) throw new BoxError(BoxError.BAD_FIELD, 'VPN app cannot require VPN access');
    -
         if (enable) {
             const config = await settings.getJson(settings.VPN_ACCESS_CONFIG_KEY);
    +        if (config?.vpnAppId === app.id) throw new BoxError(BoxError.BAD_FIELD, 'VPN app cannot require VPN access');
             const allowlist = network.parseVpnAccessAllowlist(await network.getVpnAccessAllowlist());
             if (!config?.vpnAppId && allowlist.length === 0) throw new BoxError(BoxError.BAD_FIELD, 'VPN app is not configured');
         }
    @@ -3126,6 +3133,7 @@ export default {
     
         setAccessRestriction,
         setOperators,
    +    isVpnProvider,
         setVpnAccess,
         setCrontab,
         setUpstreamUri,
    diff --git a/src/network.js b/src/network.js
    index 2d1d1e9..0ebb6d7 100644
    --- a/src/network.js
    +++ b/src/network.js
    @@ -185,7 +185,8 @@ async function setVpnAccessConfig(policy, auditSource, allowlist) {
     
             const vpnApp = await apps.get(vpnAppId);
             if (!vpnApp) throw new BoxError(BoxError.BAD_FIELD, 'vpnAppId not found');
    -        if (vpnApp.manifest.id !== constants.OPENVPN_APP_APPSTORE_ID) throw new BoxError(BoxError.BAD_FIELD, 'vpnAppId must be an OpenVPN app');
    +        if (!apps.isVpnProvider(vpnApp.manifest)) throw new BoxError(BoxError.BAD_FIELD, 'vpnAppId must be a VPN app (OpenVPN or an app with the net_admin capability)');
    +        if (vpnApp.requiresVpn) throw new BoxError(BoxError.BAD_FIELD, 'VPN app cannot itself require VPN access');
     
             validateTunnelRouting(tunnelRouting);
         }
    diff --git a/src/test/network-test.js b/src/test/network-test.js
    index ea34bd2..d7e6d18 100644
    --- a/src/test/network-test.js
    +++ b/src/test/network-test.js
    @@ -210,11 +210,53 @@ describe('Network', function () {
                 assert.equal(error.reason, BoxError.BAD_FIELD);
             });
     
    -        it('rejects non-openvpn app', async function () {
    +        it('rejects an app that cannot route traffic', async function () {
                 const [error] = await safe(network.setVpnAccessConfig({ vpnAppId: common.app.id, tunnelRouting: { mode: 'full', customCidrs: [] } }, auditSource));
                 assert.equal(error.reason, BoxError.BAD_FIELD);
             });
     
    +        describe('with a net_admin VPN app', function () {
    +            const meshAppId = 'network-mesh-vpn-app-id';
    +
    +            before(async function () {
    +                const meshManifest = { ...common.manifest, id: 'io.example.meshvpn', capabilities: [ 'net_admin' ] };
    +                const meshData = {
    +                    ...common.app,
    +                    id: meshAppId,
    +                    appStoreId: '',
    +                    installationState: constants.APP_ISTATE_INSTALLED,
    +                    subdomain: 'network-mesh-vpn',
    +                    domain: common.domain.domain,
    +                    manifest: meshManifest,
    +                    portBindings: {},
    +                    secondaryDomains: [],
    +                    redirectDomains: [],
    +                    aliasDomains: [],
    +                    containerId: 'network-mesh-vpn-container-id',
    +                    containerIp: '172.18.88.97'
    +                };
    +                await apps.add(meshAppId, meshData.appStoreId, '', meshManifest, meshData.subdomain, meshData.domain, {}, meshData);
    +            });
    +
    +            after(async function () {
    +                await network.setVpnAccessConfig(null, auditSource);
    +                await apps.del(meshAppId);
    +            });
    +
    +            it('can select it as the VPN app', async function () {
    +                await network.setVpnAccessConfig({ vpnAppId: meshAppId, tunnelRouting: { mode: 'custom', customCidrs: [] } }, auditSource);
    +                assert.equal((await network.getVpnAccessConfig()).vpnAppId, meshAppId);
    +            });
    +
    +            it('cannot select it while it requires VPN access itself', async function () {
    +                await network.setVpnAccessConfig(null, auditSource);
    +                await apps.update(meshAppId, { requiresVpn: true });
    +                const [error] = await safe(network.setVpnAccessConfig({ vpnAppId: meshAppId, tunnelRouting: { mode: 'full', customCidrs: [] } }, auditSource));
    +                assert.equal(error.reason, BoxError.BAD_FIELD);
    +                await apps.update(meshAppId, { requiresVpn: false });
    +            });
    +        });
    +
             it('rejects invalid tunnel routing', async function () {
                 const [error] = await safe(network.setVpnAccessConfig({ vpnAppId, tunnelRouting: { mode: 'full' } }, auditSource));
                 assert.equal(error.reason, BoxError.BAD_FIELD);
    

    Would you consider this, or something like it? Thanks!


  • The regime in the UK is out of control
    marcusquinnM marcusquinn
    Off-topic security

    Yookay seems to be leading the world in parody politics, now 🤷

    I expect this post is, too — but, the plausibility is the concern, as it's not beyond everything else that seems to be going on.

    Sadly, all these things would affect the poorest and least technology literate the most — as I expect would be the intent.

    Control information to control voting — by depriving the majority from understanding what they are voting for, or what their votes used to be able to stop.

    I read they are giving utility companies access to things like tax returns, pensions, home values, so they can also data-mine people for how much more they can charge them to keep the lights on. So a £ be revalued based on some algo's idea of how much you should get for it. I guess the real reason why "smart meters" were so heavily pushed.

    And, because we can chat here, that'll also be a target for the "social media" fun-police.

    Everyone submitted their Digital ID to talk about Cloudron here, yet?


  • Orbit.so - free open-source alternative to Trello, Notion, Slack, Webmail, Todoist, and similar
    marcusquinnM marcusquinn
    App Wishlist

    Now packaged as a community app (testing release):

    • https://forum.cloudron.io/topic/16266/orbit-open-source-tasks-docs-and-team-chat-in-one-workspace-with-an-mcp-server-for-ai-community-package-testing
    • https://ca.cloudron.io/app/com.marcusquinn.cloudron.orbit

    Install from:
    https://raw.githubusercontent.com/marcusquinn/cloudron-orbit-app/main/CloudronVersions.json

    Title correction: Orbit has no webmail, yet. Its Mail section shows "Coming soon" and is a preview with sample data upstream.

    Tasks, docs, team chat and the MCP server work today.

    Cloudron SSO waits on OpenID Connect support upstream: coollabsio/orbit#65.


  • Orbit – open-source tasks, docs and team chat in one workspace, with an MCP server for AI (community package, testing)
    marcusquinnM marcusquinn
    Community Packages orbit productivity wiki chat mcp

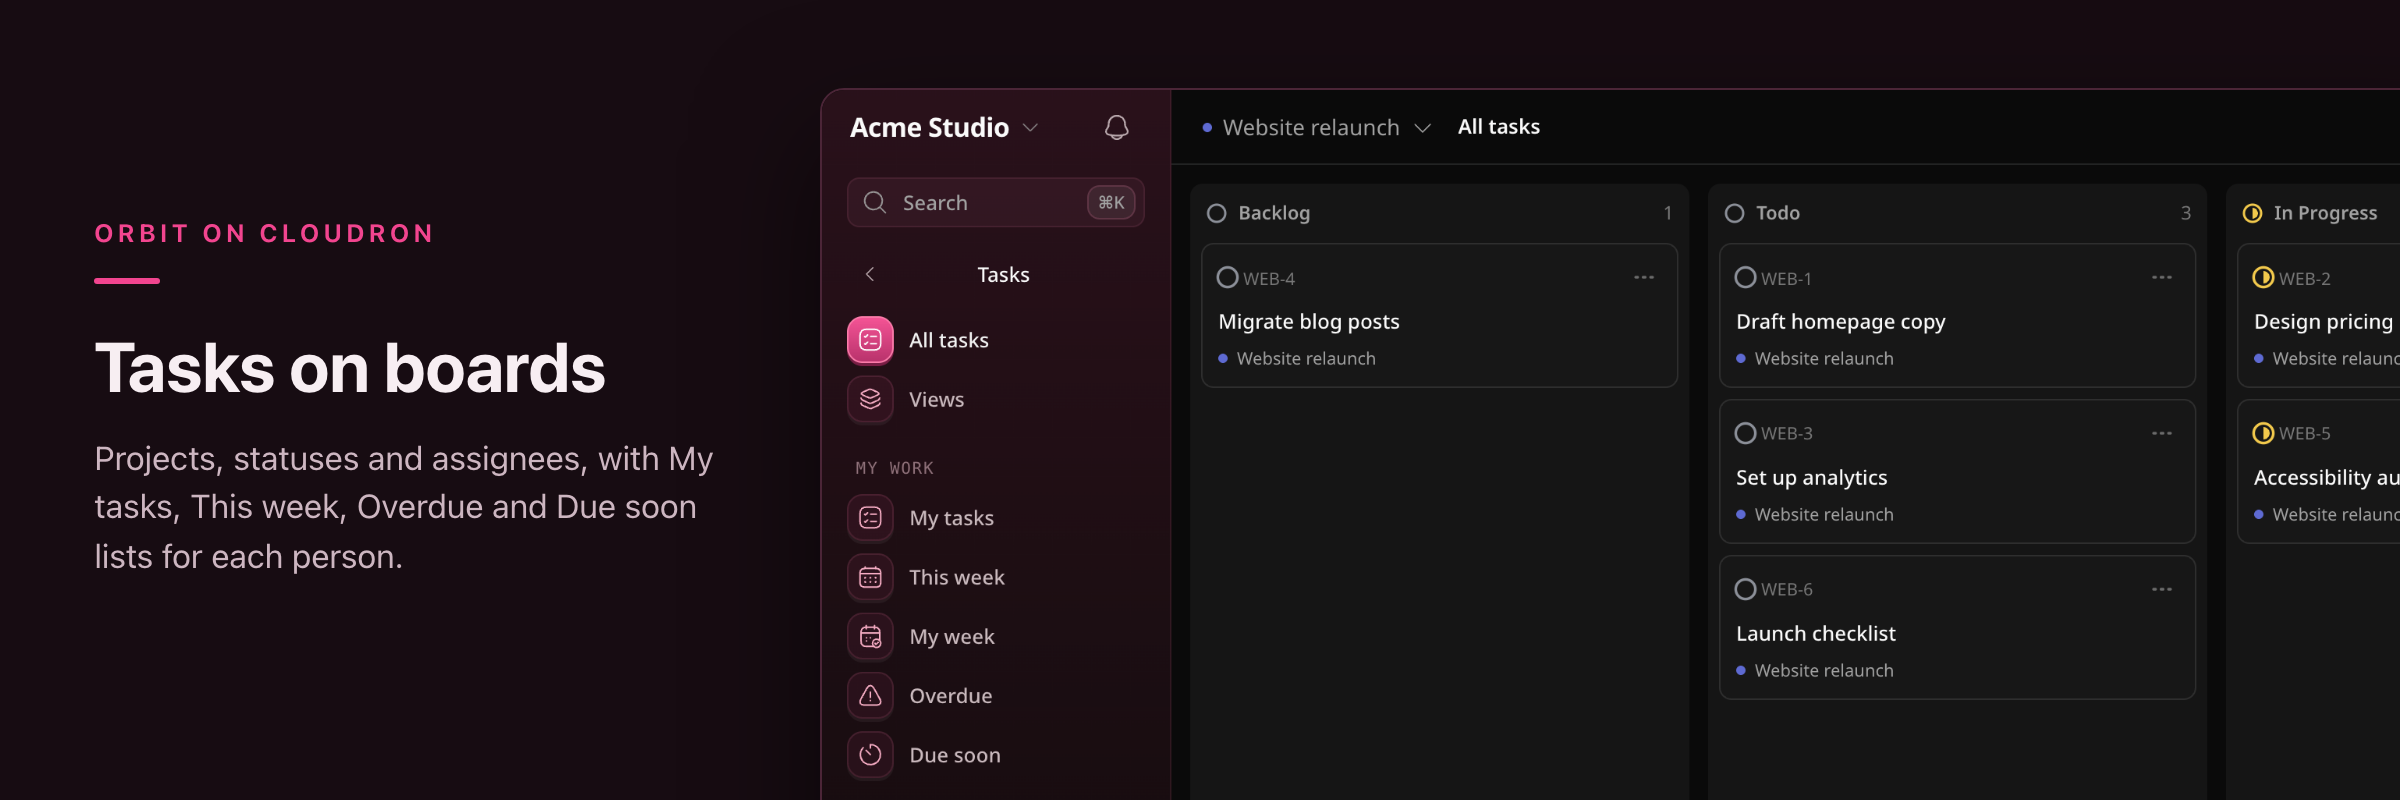
    I've packaged Orbit, an Apache-2.0 workspace for teams from the creator of Coolify, as a community app. It puts tasks (projects with list, board and timeline views), docs with live co-editing, and team chat in one app on your own server, and AI clients can work with the whole workspace through its built-in MCP server.

    Orbit tasks

    Install: add this catalog under Settings → Community apps, then install Orbit from the App Store:

    https://raw.githubusercontent.com/marcusquinn/cloudron-orbit-app/main/CloudronVersions.json
    

    or cloudron install --versions-url <that URL> --location orbit.example.com.

    What fits in with Cloudron

    • First run: Orbit prints a one-time setup link in the app's Logs, and orbit-setup-link in the Terminal prints a fresh one. Whoever opens it first becomes the root user, so use it straight after installing.
    • Outgoing mail through the Cloudron relay: invitations, password resets and test email. Orbit keeps its SMTP settings in its database and can't read them from the environment yet (coollabsio/orbit#66). Run orbit-mail-settings in the Terminal and paste the values into Admin → Email once.
    • Backups: the SQLite database (copied consistently by Cloudron), attachments and the app key are in Cloudron backups. I restored a backup into a clone, and the stored SMTP password still decrypted there.
    • Live updates through Cloudron's proxy: chat messages and doc edits appear live for other users. Orbit's sign-in rate limits see each user's real address, not the proxy's.

    Tested on Cloudron 10.1.6 with two accounts: setup, invitations, chat and doc co-editing between users, mail through the relay, MCP sign-in over OAuth, restart, backup and clone, and an app update.

    Good to know

    • No webmail yet: Orbit's Mail section is a preview with sample data upstream ("Coming soon"). Despite my wishlist title, it isn't an email client today.
    • No Cloudron SSO: Orbit doesn't support OpenID Connect yet (coollabsio/orbit#65). Sign-in is email and password or passkeys, with optional Google and GitHub sign-in.
    • Uploads: 25 MiB per file by default (ORBIT_UPLOAD_MAX_FILE_BYTES in /app/data/orbit.env). For a larger file, chat only says "Upload failed."
    • 1 GiB memory limit by default; Orbit used about 55 MiB at idle. x86-64 only for now. Requires Cloudron 10.0+.
    • Orbit is early-stage (0.2.1). The package runs upstream's release binary, pinned by digest and unmodified. Images and the catalog carry GitHub build provenance.

    Links

    • Community Apps listing:
      • https://ca.cloudron.io/app/com.marcusquinn.cloudron.orbit
    • Package, setup guide and issues:
      • https://github.com/marcusquinn/cloudron-orbit-app
    • Orbit:
      • https://github.com/coollabsio/orbit
      • https://orbit.so
    • App Wishlist post with more screenshots:
      • https://forum.cloudron.io/topic/16264/orbit.so-free-open-source-alternative-to-trello-notion-slack-webmail-todoist-and-similar

    This is a testing release, so feedback is welcome, especially from teams of several people and from anyone connecting Claude Code or another MCP client.

    I maintain the package independently of the Orbit project; please report packaging problems on the package repo rather than upstream.


  • Orbit.so - free open-source alternative to Trello, Notion, Slack, Webmail, Todoist, and similar
    marcusquinnM marcusquinn
    App Wishlist
    • Title: Orbit on Cloudron - orbit

    • Main Page: https://orbit.so/
    • Git: https://github.com/coollabsio/orbit
    • Licence: Apache-2.0 license
    • Dockerfile: Yes

    • Summary: Productivity app for teams and individuals, with an MCP for use with AI.

    • Notes: From the creator of Coolify

    • Alternative to: Trello, Notion, Slack, Webmail, Todoist, and similar
    • Screenshots:

    image.jpeg

    image.jpeg

    image.jpeg

    image.jpeg

    image.jpeg

    image.jpeg

    image.jpeg

    image.jpeg

    image.jpeg

    image.jpeg

    image.jpeg

    image.jpeg

    image.jpeg

    image.jpeg


  • Community Apps listing: use packageUrl for the Package link
    marcusquinnM marcusquinn
    Community Packages

    The CLI changelog says "Use packageUrl/packagerName/packagerUrl", and the manifest format accepts packageUrl from minBoxVersion 10.0.0. The ca.cloudron.io listing doesn't read it yet. Both the "By <packagerName>" link and the "Package" link come from packagerUrl.

    Example: Warmbly 0.1.2 is published with "packagerUrl": "https://github.com/marcusquinn" and "packageUrl": "https://github.com/marcusquinn/cloudron-warmbly-app". Its listing at https://ca.cloudron.io/app/com.warmbly.cloudronapp still links Package to the profile.

    Could the listing use packageUrl for the Package link when it's set, and fall back to packagerUrl? Then "By" can link the maintainer and "Package" the source repo. Until then I've set packagerUrl to each package's repository.

    A related trap for packagers: Cloudron 9.x rejects packageUrl anywhere in CloudronVersions.json. One entry with it stops 9.x servers reading the whole catalog, even entries that have minBoxVersion below 10. Adding it effectively ends 9.x support for that catalog.


  • Warmbly - free open-source alternative to Warmly, Instantly, Apollo, SmartLead, ListKit, Lemlist, ZoomInfo, Mailreach, WarmForge etc
    marcusquinnM marcusquinn
    App Wishlist

    There's also a case for just using the email warmup features on Cloudron, especially when starting with a fresh IP and domains for self-hosted email and needing to build reputation and check all deliverability setup needs.


  • Warmbly - free open-source alternative to Warmly, Instantly, Apollo, SmartLead, ListKit, Lemlist, ZoomInfo, Mailreach, WarmForge etc
    marcusquinnM marcusquinn
    App Wishlist

    @robi it's like the apps listed in the alts. generally use this to scale cold-emailing with best-practice for whatever you have to offer or ask. Daniel Fazio on YouTube prob the best explainers of how.


  • Warmbly - free open-source alternative to Warmly, Instantly, Apollo, SmartLead, ListKit, Lemlist, ZoomInfo, Mailreach, WarmForge etc
    marcusquinnM marcusquinn
    App Wishlist

    Now packaged as a community app. Details here:

    • https://forum.cloudron.io/topic/16229/warmbly-open-source-cold-outreach-and-email-warmup-campaigns-unified-inbox-crm-with-cloudron-sso-and-cloudron-mail

  • Warmbly – open-source cold outreach and email warmup (campaigns, unified inbox, CRM) with Cloudron SSO and Cloudron Mail
    marcusquinnM marcusquinn
    Community Packages

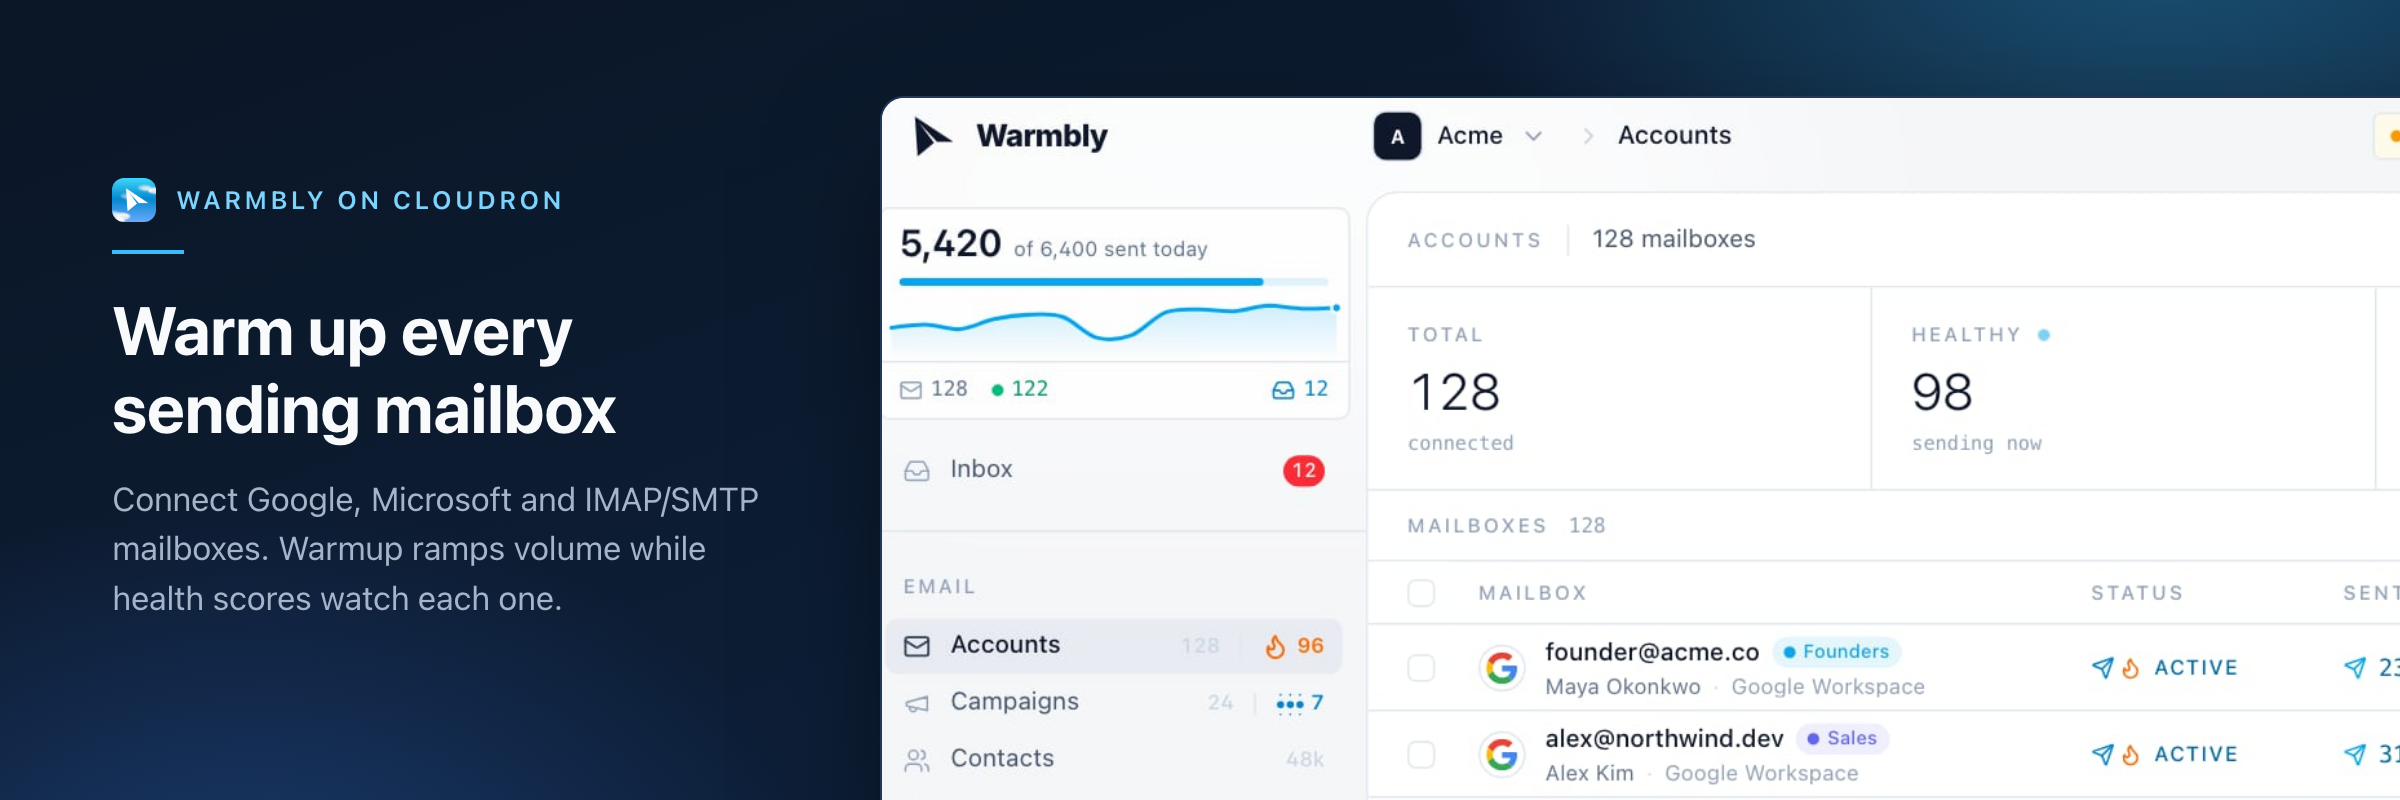
    I've packaged Warmbly, an Apache-2.0 platform for B2B cold outreach, as a community app. Connect your sending mailboxes and run multi-step campaigns across them, with warmup, a unified inbox for every reply, a CRM, hosted lead-capture forms and open/click tracking on your own tracking domain.

    Warmbly mailboxes and warmup

    Install: add this catalog under Settings → Community apps, then install Warmbly from the App Store:

    https://raw.githubusercontent.com/marcusquinn/cloudron-warmbly-app/main/CloudronVersions.json
    

    or cloudron install --versions-url <that URL> --location warmbly.example.com. The installer asks for four secondary domains: API, admin panel, tracking and forms.

    What fits in with Cloudron

    • Single sign-on, and the first sign-in claims it: open the app and choose Continue with your Cloudron. You don't need to type an email or password, and the first person to sign in becomes the owner and platform admin. Until then, password sign-ups are closed, so nobody can claim a fresh install before you do. After that, the app's access control decides who gets in. Password sign-up stays invitation-only.
    • Platform email (sign-in codes, password resets, invitations, digests) goes through the Cloudron mail relay.
    • Sending mailboxes on Cloudron Mail work over IMAP/SMTP. Gmail and Microsoft 365 work with your own OAuth clients (the README has the redirect URIs).
    • Tracking domains: use a separate registered domain for opens, clicks and unsubscribes. Customers' own tracking domains (a CNAME to yours) are added as aliases of the app, so Cloudron issues their certificates.
    • The whole self-host stack (API, event consumer, mailbox worker, tracking, forms, realtime gateway and NATS JetStream) runs in one container on the PostgreSQL and Redis addons. Data and encryption keys are in Cloudron backups.

    Good to know

    • 2 GiB memory default; raise it for many mailboxes. Requires Cloudron 9.1+.
    • Billing, update checks, CAPTCHA and product analytics are off. It runs on a single node; upstream's multi-node worker fleet isn't used.
    • The dashboard updates live through the API domain. Upstream's CLI event stream and SDKs can't discover the realtime socket on this package yet.
    • The image uses upstream's release images, pinned by digest, plus one small patch (the first Cloudron sign-in becomes owner). The patch is in the repo, and I'd like to upstream it.
    • Images and the catalog carry GitHub build provenance.

    Links

    • Package, setup guide and issues:
      • https://github.com/marcusquinn/cloudron-warmbly-app
    • Warmbly:
      • https://github.com/warmbly/warmbly
    • Docs:
      • https://docs.warmbly.com
    • App Wishlist post with further info and screenshots:
      • https://forum.cloudron.io/topic/16228/warmbly-free-open-source-alternative-to-warmly-instantly-apollo-smartlead-listkit-lemlist-zoominfo-mailreach-warmforge-etc

    This is a first release, so feedback is welcome, especially on deliverability with Cloudron Mail mailboxes and on tracking-domain setups.

    I maintain the package independently of the Warmbly project; please report packaging problems on the package repo rather than upstream.


  • Warmbly - free open-source alternative to Warmly, Instantly, Apollo, SmartLead, ListKit, Lemlist, ZoomInfo, Mailreach, WarmForge etc
    marcusquinnM marcusquinn
    App Wishlist
    • Title: Warmbly on Cloudron - warmbly

    • Main Page: https://warmbly.com/
    • Git: https://github.com/warmbly/warmbly
    • Licence: Apache-2.0 license
    • Dockerfile: Yes
    • Demo:

    • Summary: CRM for cold-email outreach to legitimate B2B prospects

    • Notes: Seems to be from the creators of OpenDesk. Will get this packaged, and share when ready...

    • Screenshots:

    image.jpeg

    image.jpeg

    image.jpeg

    image.jpeg

    image.jpeg

    image.jpeg

    image.jpeg

    image.jpeg

    image.jpeg

    image.jpeg

    image.jpeg

    image.jpeg

    image.jpeg

    image.jpeg

    image.jpeg

    image.jpeg

    image.jpeg


  • Security issue thread - PHP and eMudhra cert compromise
    marcusquinnM marcusquinn
    Announcements

    @jadudm it came from this bit of banter:

    • https://forum.cloudron.io/post/131061

  • Security issue thread - PHP and eMudhra cert compromise
    marcusquinnM marcusquinn
    Announcements

    Always thought this about Cloudron; anything that's not supposed to be a public website or app should be behind a mesh vpn, hence this research back in Feb 2022, and hope that Netbird can be a support app for vpn gating cloudron apps:

    • https://forum.cloudron.io/topic/7571/netbird-foss-noconf-mesh-vpn-using-wireguard-alternative-to-zerotier-tailscale-omniedge-netmaker-etc

    Security through invisibility. Buys more time for patching these incidents.


  • OpenDesk – open-source helpdesk (shared inbox, live chat, help center) with Cloudron SSO and Cloudron Mail
    marcusquinnM marcusquinn
    Community Packages

    don't know who made the request, but there's a new release for you:

    • https://github.com/marcusquinn/cloudron-opendesk-app

  • Lots to patch — point your AI at this and ask it what it can patch in the meantime
    marcusquinnM marcusquinn
    Discuss

    @andreasdueren yup — been pointing claude at that too — looks like website spammers are gonna be making a right mess for a while


  • Mask addon credentials in app task logs
    marcusquinnM marcusquinn
    Support services logs

    When an app is installed or updated, the app log includes lines like:

    services: Setting postgresql addon config to [{"name":"CLOUDRON_POSTGRESQL_URL","value":"postgres://<user>:<password>@postgresql/<db>"},{"name":"CLOUDRON_POSTGRESQL_PASSWORD","value":"<password>"},...]
    services: Setting sendmail addon config to [...{"name":"CLOUDRON_MAIL_SMTP_PASSWORD","value":"<password>"}...]
    

    Only admins and operators can see these (including AI sessions), and they can already read the environment, so this isn't an access problem.

    But app logs are what people paste into forum posts and support requests, and AI sessions logs can be mined — and these lines sit in the middle of normal startup output.

    Could the values be masked in those debug lines (for example "value":"***" for passwords and URL userinfo), keeping just the variable names?


  • Lots to patch — point your AI at this and ask it what it can patch in the meantime
    marcusquinnM marcusquinn
    Discuss
    • https://x.com/DanielLockyer/status/2112631992118374491?s=20

    image.jpeg

    • https://x.com/astuyve/status/2112559796914167931

    image.jpeg

    • https://thecybersecguru.com/news/emudhra-ca-compromise/

    basically, everything online


  • OpenDesk – open-source helpdesk (shared inbox, live chat, help center) with Cloudron SSO and Cloudron Mail
    marcusquinnM marcusquinn
    Community Packages

    @luckow andddd claude says:

    Found it: 0.1.0–0.1.2 shipped an upstream bug (fixed in https://github.com/useopendesk/opendesk/pull/52) where a finished mailbox sync stopped the next one from being queued for about 24 hours, so a mailbox synced once and then went quiet. 0.1.3 is now in the catalog with the fix. Update from the dashboard and syncing resumes within a minute, with no need to re-add the mailbox. opendesk checks every minute on its own, which is why there's no frequency setting or manual sync button. Thanks for the report!


  • OpenDesk – open-source helpdesk (shared inbox, live chat, help center) with Cloudron SSO and Cloudron Mail
    marcusquinnM marcusquinn
    Community Packages

    @luckow seem it is an upstream bug. just updating the package with the latest version that suggests it's fixed. i'm not using the app yet in any meaningful sense, so still early days, but does look promising compared to the alternatives when you look at the way they're mixing in ai.


  • Tailscale - decentralised noconf Mesh VPN using Wireguard, alternative to ZeroTier etc
    marcusquinnM marcusquinn
    App Wishlist

    @fbartels I packaged the headless server:

    • https://forum.cloudron.io/topic/16152/headscale-self-hosted-tailscale-control-server-with-cloudron-sso-and-a-built-in-derp-relay

    You can ask your AI for any explainers, help with setup (instructional or directly with ssh), and diagnosing any issues.

    I don't particularly use it, but should all work, though — and use Netbird if you want a GUI and like their UX.

  • Login

  • Don't have an account? Register

  • Login or register to search.
  • First post
    Last post
0
  • Categories
  • Recent
  • Tags
  • Popular
  • Bookmarks
  • Search