@girish thanks, the queue is empty and the dovecot.log only has yesterday and todays events in there. I'll ask the people to do a test, they switched to manual bcc as a workaround atm
What is the use case to prevent internal routing?
But if you set up an external MX record and add that MX host to your SPF also (so Cloudron will accept incoming), then I think it does what you want?
Just to let you know, I still get the error " Connection to the POP3 server is failing with an authentication error. Please check your POP3 settings." in the admin dashboard. Though everything looks to work perfectly fine.
TTL issue ? I mean, this symptom lasted a very long time (a full year I'd say). Not seen since early June though. Maybe the "odd DNS issue" then. I guess this can be closed.
@james Yes it’s technically a feature request. I only threw it in here since it seemed like Girish was already making adjustments to the filtering in the mail event log viewer. If you’re okay forking it to a feature request, that’s totally fine.
your config.production.json should work as it is identical to the solution here:
https://forum.ghost.org/t/unable-to-invite-new-admin-users-to-account-without-mailgun-setup/56711/11
I had tried it and it is working for me. by default if you set up ghost.example.com cloudron should set up an email account ghost.app@example.com for you, you should use ghost.app@example.com instead of newsletter@example.com.
Hi @fbartels
You're right, double checked and it always defaults to smtp. instead of .my
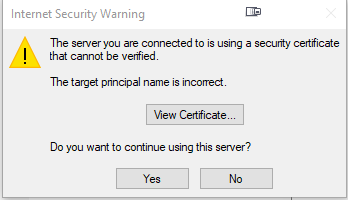
When manually changing on both PC and Mobile, the SMTP accounts can be added without the certificate error!
Thanks Everyone!
@mrhakash said in Outbound Emails Queued — NXDOMAIN Error and Local DNS Resolution Issue:
dig @127.0.0.1 gmail.com mx returns:
connection refused
You have to check host -t MX gmail.com 127.0.0.150 . Can you also run cloudron-support --troubleshoot for hints?
Here the issue was that the e-mails have been moved to the new cloudron server only partially, and the new folder wasn't created in this case, so when I tried to move this in Thunderbird, it failed.
So, this is solved now
@scooke said in Every Cloudron instance sets a DKIM entry. Is this good or bad or necessary?:
why use ai when we already have Real Intelligence here.
Limited time and resources of humans?
@jdaviescoates said in URGENT:
In a post on an originally unrelated thread about IPv6 issues @Gengar posted this link https://www.spamhaus.com/resource-center/successfully-accessing-spamhauss-free-block-lists-using-a-public-dns/ which I think explains what's going on with all these false positive spamhaus issues people are having:
The TL;DR seems to be: fill in this form https://www.spamhaus.com/free-trial/sign-up-for-a-free-data-query-service-account/
@jdaviescoates said in Cloudron seems to have changed to set-up ?all SPF records instead of ~all - why?:
whereas only my newer ones have ?all
I checked some domains on my Cloudron and noticed one has -all where all others have ~all. Then I realised that one was a recently transferred domain that was already 'working' and obviously the previous hoster had it like this, Cloudron didn't touch it when "importing" it.
A homemade problem. We have refactored our Ansible role. It has installed an MTA that was previously started as Cloudron's mail service. After uninstalling the MTA, everything works as expected.